
 ItalianoIT
 DeutschDE
 EspañolES
 PortuguêsPT
 FrançaisFR
 РусскийRU
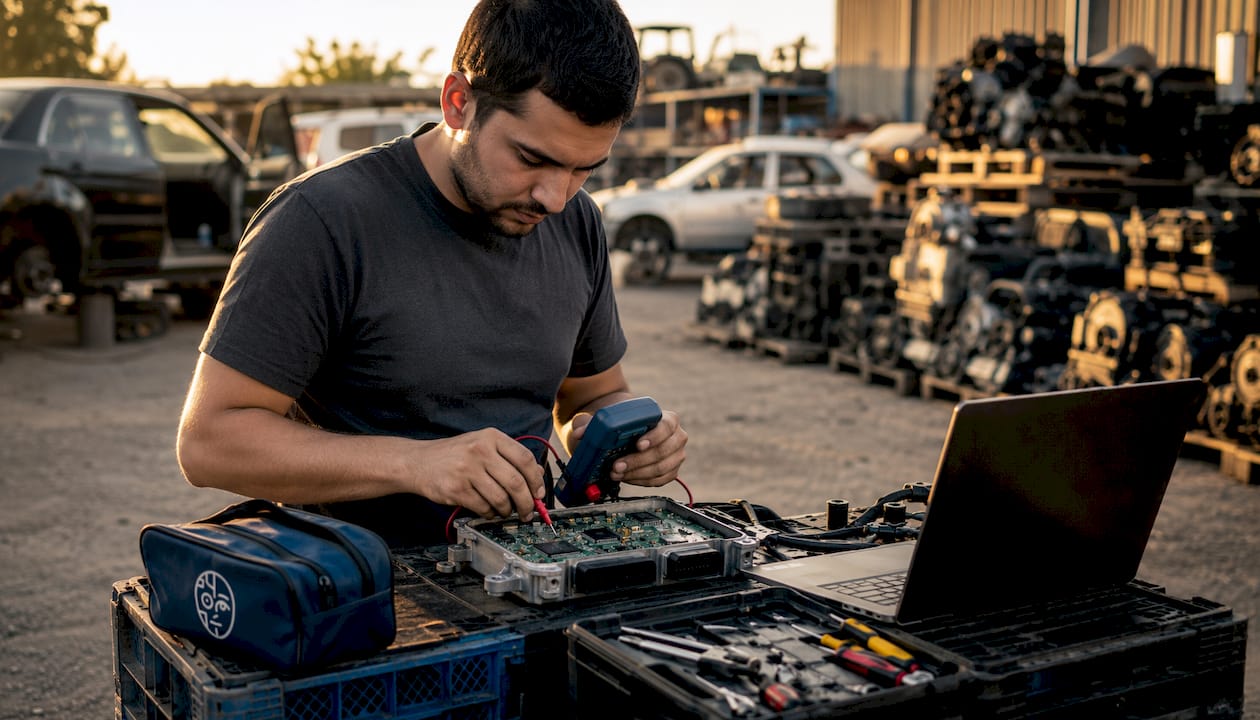
ECU file security is the protection of calibration binaries, supporting documents, credentials and workflow records throughout their lifecycle. For an independent workshop, the most practical controls are access restriction, secure transfer, reliable backups, file-integrity checks, account protection and documented handling procedures. OEM-level measures such as signed boot chains, HSM-backed keys and anti-rollback counters belong primarily to ECU and tool manufacturers, not to ordinary workshop file handling.
Core best practices for ECU file security in workshops
Protecting ECU calibration files starts with three non-negotiable controls: strict data classification, cryptographic signing, and role-based access. Every other measure builds on these. Without them, even the most sophisticated flashing workflow is exposed.
- Classify files by sensitivity: separate customer originals, tuned files, internal templates and confidential project data. Use approved storage appropriate to the workshop’s risk and contractual obligations.
- Restrict access by role and job: technicians should only access the files needed for their work, with periodic review of accounts and shared folders.
- Verify integrity and authenticity where supported: workshops should use checksums, hashes, signed packages or tool-native verification when available. OEM signing keys are generally not controlled by independent tuners.
- Keep useful audit records: record uploads, downloads, revisions, operator notes and delivery times where the chosen platform supports it.
- Prefer managed transfer channels: use authenticated portals or controlled sharing methods instead of public links or poorly tracked attachments.
- Protect credentials and secrets: do not keep passwords, API keys or recovery credentials in plaintext. HSMs and secure elements are appropriate where the tool or infrastructure supports them.
- Review the workflow regularly: remove obsolete accounts, update tools, check backups and verify that sharing permissions still match current staff and projects.
Pro Tip: Protect the root of trust first. Unsigned bootloader images or missing anti-rollback counters render every downstream control useless, regardless of how well the rest of the workflow is locked down.
Common technical security pitfalls in ECU file handling
Many security incidents in workshop environments arise from ordinary operational weaknesses such as reused passwords, uncontrolled sharing, lost devices, stale accounts and poor backup discipline rather than advanced attacks.
- Missing integrity checks and rollback protection: can be serious on platforms that support signed software, but these controls are implemented differently across ECUs and are not always managed by the workshop.
- Password-only protection is bypassable. UI-level password restrictions on tuning software can be circumvented by skilled operators when backend encryption and code-signing enforcement are absent. Passwords are an access hint, not a security boundary.
- Plaintext master keys on flashing hardware are a direct IP extraction path. Storing raw keys in MCU flash or on diagnostic tool storage means an attacker with physical access to the tool can recover calibration data without ever touching the ECU files themselves.
- Unsecured transfer channels such as email attachments or public cloud links leave no proof of delivery, no revocation capability, and no identity record. A single forwarded link can expose a proprietary Stage 2 calibration to an unintended recipient permanently.
- Weak diagnostic-access controls: security-access timing, counters and negative responses are ECU implementation details. ISO 14229 defines services and response behavior, but not one universal lockout policy for every ECU.
- Poor recovery strategy: interrupted writing can corrupt an ECU. A/B partitions are common in some embedded systems, but many automotive ECUs instead rely on boot recovery, service mode or external programming.
Pro Tip: Securing the flashing tool is as critical as securing the file. An attacker who extracts keys from an Alientech KESS3, AutoTuner, Magic Motorsport, CMD, Dimsport, or PCMFlash interface gains access to every calibration that tool has ever processed.

Moving beyond passwords: zero-trust and data-centric security
Password protection alone is not a security model. It is a friction layer. Professional workshops handling Bosch, Continental, Delphi, Marelli, Denso, Siemens, Keihin, and ZF ECU files need controls that follow the data, not just the door.
- Zero-trust applied to ECU file management means every access request is verified at the point of request, regardless of whether the requester is inside the workshop network. Never trust a session; always verify identity and permission scope.
- Data-centric security tracks, encrypts, and controls files throughout their entire lifecycle and regardless of where they are stored. Moving beyond passwords to this model is the standard recommendation for protecting sensitive CAD and calibration IP.
- Least-privilege and need-to-know scoping at the project level means a technician working on a Bosch MED17 file for one customer cannot access a Continental Simos calibration for another, even within the same workshop system.
- Cryptographic integrity verification: may use signatures, MACs, hashes or tool-specific containers. The correct method depends on the ECU and delivery platform; HMAC-SHA256 is not a universal automotive requirement.
- Limit diagnostic authorization windows: where supported, keep privileged sessions short and use only the services required for the job. Exact behavior depends on the ECU security implementation.
- Audit telemetry and anomaly detection: can support internal governance and supplier requirements. TISAX or UNECE obligations apply only where the organization and contractual scope make them relevant.
Lifecycle management strategies for ECU file security
A calibration file is a liability from the moment it is created until the moment it is securely disposed of. Lifecycle management is the discipline that keeps that liability controlled at every stage.
| Lifecycle Stage | Required Control | Evidence Artifact |
|---|---|---|
| Creation | Data classification label applied at file creation | Labeled file samples or metadata export |
| Storage | Approved repository only; no unencrypted local copies | Repository access group export |
| Access | RBAC with documented approval and periodic review | Access request and approval records |
| Transfer | Managed channel with identity log and revocation | SFTP logs or managed sharing audit trail |
| Flashing | Signed manifest verified before write; atomic update | Signed release bundle with version metadata |
| Disposal | Secure deletion with documented sign-off | Deletion confirmation record |
Version control and hashes help detect unexpected changes, but only if reference values and file history are themselves protected. A mismatch should trigger review rather than an automatic assumption of malicious modification.
Incident response must be pre-planned, not improvised. When a confidential ECU file is exposed, the response sequence is: isolate the affected share, revoke access tokens, review audit logs to scope the exposure, notify affected parties per contractual obligations, and document the full incident in the exception register.
Professional tools and practical resources for ECU file security
The right tools enforce security controls at the workflow level, not as an afterthought.
TuningBot provides a professionally managed ECU file delivery platform supporting all major ECU brands including Bosch, Continental, Delphi, Marelli, Denso, Siemens, Keihin, and ZF. File transfers occur through a structured, auditable workflow with real engineer oversight, replacing the ad-hoc email and consumer cloud methods that create IP exposure. The Continental ECU file guide published by TuningBot covers security protocols and file structure handling for professional tuners working with Simos, SID, and KESS3 configurations.
Hardware security modules can protect signing keys and other sensitive credentials in larger or OEM-linked environments. Small workshops may instead rely on secure cloud identity, encrypted storage and tool-managed credentials, depending on their risk profile.
Flashing tools should be kept on supported firmware and protected with strong account and workstation security. Updates may provide protocol, reliability and security fixes, but the manufacturer’s release notes should guide each update decision.
TuningBot’s secure file transfer workflow documentation provides a practical reference for workshops building or auditing their own file handling procedures.
For an example of vehicle-bound storage-key concepts in an automotive platform, see the official Android Automotive documentation on vehicle-bound encryption key derivation. This is a platform-specific reference, not a universal ECU implementation requirement.
TuningBot’s managed ECU and TCU file workflow
TuningBot provides a structured file-submission workflow for professional workshops using tools such as Alientech KESS3, AutoTuner, Magic Motorsport, CMD, Dimsport and PCMFlash. A managed portal reduces the risks associated with uncontrolled attachments and public sharing links, but the workshop must still protect its accounts, local downloads and vehicle records.
Before ordering, workshops can check ECU and TCU Service Coverage, review the public Price List and browse the available ECU services.
The original file can be submitted through Tune Your File without prepaid credits. Workshops should retain the original read, record the ECU ID and store each returned revision with clear version information.
For related guidance, see the online tuning file workflow and the Continental ECU file guide.
The security gap most workshops still ignore
The automotive tuning industry has made real progress on file encryption and access control. The gap that persists is tool security. Workshops invest in securing the files but leave the flashing hardware essentially open. An Alientech KESS3 or similar interface sitting on a bench with unprotected credentials is a complete bypass of every file-level control upstream of it.
Zero-trust and hardware-rooted security are increasingly relevant in OEM and regulated supply chains. Independent workshops should not claim TISAX or UNECE compliance unless those frameworks genuinely apply to their assessed role and documented processes.
The more consequential trend is vehicle-bound encryption seeds and OTA update security. As ECUs from Bosch, Continental, and Denso increasingly tie calibration keys to vehicle hardware identifiers, the attack surface shifts from file repositories to the provisioning process itself. Workshops that understand this now, and build HSM-backed signing workflows accordingly, will be positioned to handle next-generation ECU architectures without rebuilding their security posture from scratch.
The technical foundation is not complex. Protect the root of trust, enforce least-privilege access, use auditable transfer channels, and keep tool firmware current. The culture piece is harder: security must be a standing workflow requirement, not a response to an incident.
FAQ
What encryption standard should ECU files use?
Independent workshops generally cannot sign ECU images with OEM private keys. They should use the integrity and authorization mechanisms supported by the tool, ECU and legitimate file provider, while keeping confidentiality and access credentials separate.
Why is password protection alone insufficient for ECU files?
UI-level passwords can be bypassed when backend encryption and code-signing enforcement are absent. Robust ECU data protection requires cryptographic signing, role-based access control, and audit logging in addition to any password layer.
How should ECU files be transferred securely between workshops?
Use managed file-sharing platforms that log recipient identity, download timestamps, and access duration. Ad-hoc methods such as unencrypted email or consumer cloud links provide no revocation capability and leave no auditable record.
What is the role of hardware security modules in ECU file security?
HSMs store device keys, monotonic counters, and signing credentials in tamper-resistant hardware, preventing key extraction from MCU flash. AUTOSAR Crypto/HSM integration is the standard production pattern for secure ECU programming workflows.
Which automotive security frameworks apply to ECU file handling?
TISAX is an assessment and exchange mechanism used in the automotive supply chain, not a universal law for every workshop. UNECE software-update rules primarily apply to vehicle manufacturers and type-approval responsibilities, though their expectations can influence suppliers and service partners.
Key Takeaways
Effective ECU file security requires cryptographic signing, hardware-backed key storage, and auditable access controls applied consistently across the entire file lifecycle.
| Point | Details |
|---|---|
| Sign before you flash | Always verify OEM-signed images in a validated bootloader; unsigned images invalidate all other controls. |
| Hardware key storage | Store master keys and monotonic counters in an HSM or secure element, never in plaintext MCU flash. |
| Role-based access | Restrict file access by role and project scope, with documented approvals and periodic access reviews. |
| Auditable transfers | Use managed channels that log recipient identity and access duration; prohibit unencrypted email for ECU file sharing. |
| Lifecycle governance | Apply data classification at creation and maintain version control with checksums through to secure disposal. |